Recover the right AD object. Review changes before applying them.
Prepare the AD catalog point, object identity, attribute difference and scoped restore delegation; assess Recycle Bin and System State objectives separately.
Attribute restore on an existing object, creating a new object from a catalog and recovering a deleted object through Recycle Bin have different identity outcomes. Creating a new object does not recover its old SID/GUID or password hash. This guide covers online object/attribute assessment, not full DC/forest or destructive System State apply.
Screenshots were captured from the actual lab interface on 16 October 2026. The interface is in English; explanations follow your selected language. Resource names, dates and settings are examples; use values for your own environment.
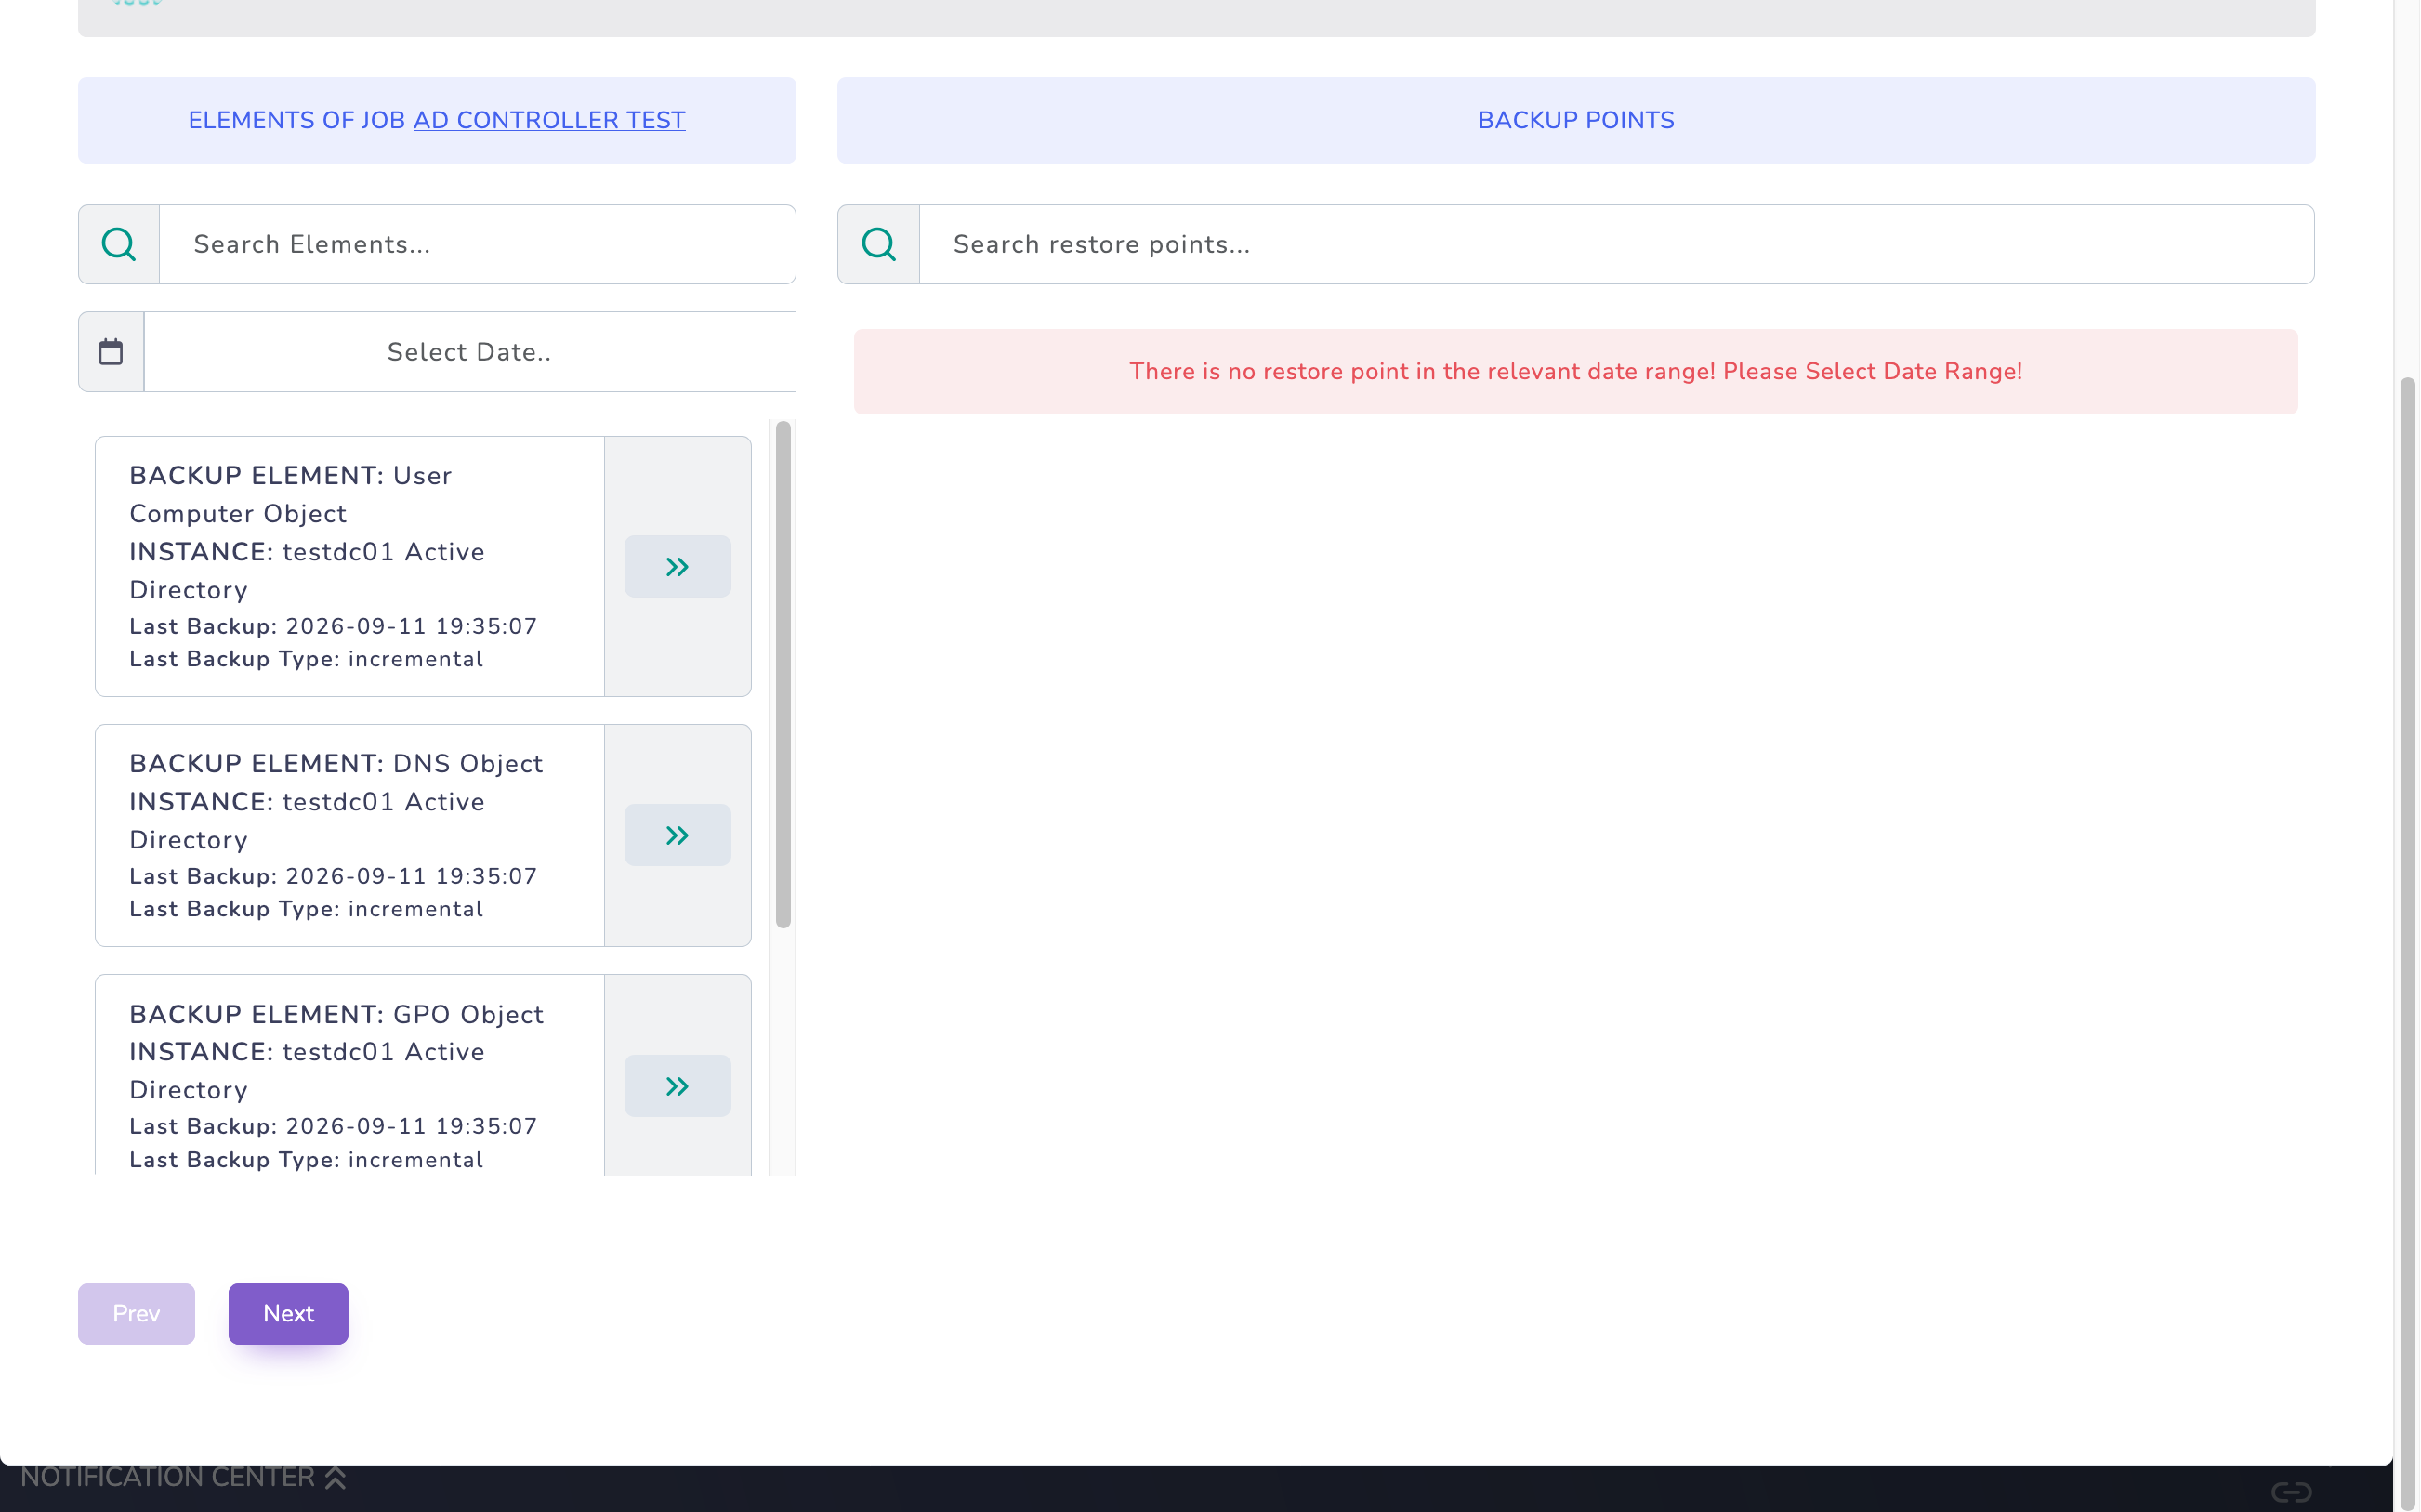
Validation limit: existing catalog items were viewed; no recovery point was found for Attributes or User Computer Object in the current date range. No object/attribute target preview was captured. No AD writes, object creation/deletion, permission changes or System State apply were performed. Historical lab acceptance does not apply automatically to every installed release.
Correct backup ID, domain, DC and catalog time
Matching target object GUID/SID, DN and OU
Restore privileges scoped to the selected operation/attribute
Dry-run/diff, change approval and final validation plan
01
1. Identify recovery type and identity
Distinguish attribute rollback on an existing object, deleted-object reanimation/Recycle Bin recovery and creation of a new object from a catalog. Record target GUID/SID, DN and OU. Protected accounts, group membership, passwords and SPNs are outside a simple description test.
Expected result
Identity-preservation expectations and operation type are explicit.
02
2. Select the AD record and recovery point
Find the correct AD test job in Home → Backups → Backup List. Use Action → Restore to inspect instance/item and Full/dependent points. Compare domain, item type and time. Last Backup or an object list in the catalog does not prove live target connectivity or successful recovery.
RESTORE → Step One: User Computer Object, DNS Object, GPO Object and Attributes catalog items. No point was found for the selected item in the current date range; no restore preview was opened through Next. Enlarge ↗
Expected result
The correct source item and point are identified.
03
3. Inspect one test object and attribute
Use search in User Computer Object or the release-specific Attribute Restore screen to find only the test object. Compare GUID and target DN; avoid Select All. Record current and backed-up values. DNS/GPO recovery requires separate acceptance from user/computer operations.
Expected result
The scope is one object and the selected attribute.
04
4. Validate dry-run and scoped permissions
In the matching granular restore release generate a dry-run/diff and inspect only the intended attribute change. Delegate permissions for the operation, such as WriteProperty on an existing object or class-specific CreateChild for a new one. Deleted Objects and Reanimate rights for Recycle Bin/tombstone require separate acceptance. A backup token does not imply AD write access; do not publish the confirmation token.
Expected result
The plan and permissions cover only the intended change.
05
5. Apply the approved change once
Compare source backup ID, object identity, attribute, old/new value and target with the summary. Do not treat a legacy bulk Restore screen without dry-run as a safe preview; use the matching validated operation workflow with the technical team. Apply the final restore only to the approved test object; account enablement and password reset are not automatic parts of this step.
Expected result
One traceable test change is created.
06
6. Compare object and operation results
Compare task/audit results with the target AD attribute value. For an existing-object attribute restore verify unchanged GUID/SID and no unexpected differences in a repeated dry-run. Group membership is assessed through member on the target group; do not assume direct writes to memberOf. A success notification alone does not establish acceptance.
Expected result
Target value, identity and audit record agree.
07
7. Keep System State and forest plans separate
Document object acceptance with backup ID, release, target and changed attributes; have the responsible administrator remove temporary test delegation. System State/authoritative/DSRM and forest recovery need an isolated/fenced environment, a separate recovery identity and a release-appropriate specialist procedure. An online object test does not establish full domain/forest recovery support.
Expected result
Object acceptance and broader recovery scope are recorded separately.
COMMON QUESTIONS
Is Recycle Bin recovery a restore from the backup archive?
No. Recycle Bin uses the directory’s deleted-object mechanism. It differs in data path and acceptance from archive-based attribute/object recovery and System State operations.